Compliance‑First: How Dedicated Servers Are Redefining Security for Regulated Industries
When I first stepped onto the floor of a Fortune‑500 financial firm, the air was thick with one word: compliance. Every conversation, every diagram, every vendor questionnaire revolved around meeting a maze of regulations—PCI‑DSS, HIPAA, GDPR, and a handful of industry‑specific mandates. The IT team’s biggest headache? Finding a hosting solution that could give them iron‑clad security, crystal‑clear data‑sovereignty, and the flexibility to innovate without stepping on legal landmines.
Fast forward a few years, and I’ve seen a decisive shift: regulated enterprises are gravitating back to dedicated server hosting. Not because the cloud is broken, but because a single‑tenant environment provides a level of control and auditability that multi‑tenant public clouds simply can’t match out‑of‑the‑box.
The Myth of “One‑Size‑Fits‑All” Cloud
Cloud providers love to tout elasticity and pay‑as‑you‑go pricing. Those are compelling for startups and dev‑centric teams, but when you’re juggling thousands of compliance checkpoints, elasticity becomes a liability. Imagine a scenario where a regulatory audit demands proof of data residency for the past 12 months. In a public cloud, data may be silently migrated across regions for load balancing, leaving you scrambling to produce immutable logs.
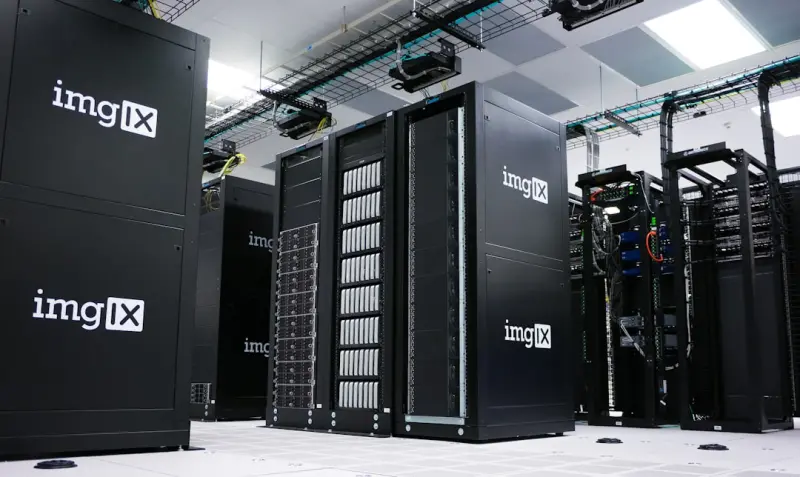
Dedicated servers, by contrast, sit in a known rack, in a known datacenter, under a known jurisdiction. The physical isolation means you can enforce hardware‑level encryption, network segmentation, and access controls that are auditable down to the BIOS level. This is the kind of granularity auditors love to see.
Zero‑Trust Architecture Starts with the Server
Zero‑trust is no longer a buzzword; it’s a baseline requirement for sectors like healthcare, finance, and government. The core principle is “never trust, always verify.” While software‑defined firewalls and identity‑centric policies are essential, the foundation must be a server that you can physically trust.
- Hardware Root of Trust: With dedicated hardware, you can enable TPM (Trusted Platform Module) chips and secure boot sequences that guarantee the server boots only trusted firmware.
- Micro‑Segmentation: By allocating each workload its own dedicated NIC or VLAN, you prevent lateral movement—a common vector in ransomware attacks.
- Full‑Disk Encryption: Since you control the key management lifecycle, you can implement customer‑managed keys (CMKs) that never leave your premises.
These capabilities are difficult to replicate in a shared environment where the underlying hypervisor is managed by a third party.
Data Sovereignty: The Legal Compass You Can’t Ignore
Regulations are increasingly dictating not just what data you store, but where you store it. The EU’s GDPR, Brazil’s LGPD, and the US’s emerging data‑localization statutes each have strict residency requirements. With a dedicated server hosted in a compliant data center—say, a Tier III facility in Frankfurt—you have a clear answer to “where is my data?”
In contrast, a public cloud’s “region” abstraction can be misleading. A “European” region might still spin up resources in a neighboring country for redundancy, potentially violating strict data‑location clauses. Dedicated servers eliminate that ambiguity.
Audit Trails That Actually Mean Something
Compliance audits demand more than just screenshots of dashboards. Auditors want tamper‑evident logs that can be traced back to a specific piece of hardware at a specific time. With dedicated servers you can:
- Implement immutable logging at the OS level (e.g.,
auditdon Linux) and forward logs to a secure SIEM. - Leverage hardware‑based logging modules that write to write‑once‑read‑many (WORM) storage.
- Integrate with third‑party compliance platforms that require cryptographic signatures on log files.
These measures provide a rock‑solid chain‑of‑custody that satisfies auditors for PCI‑DSS, HIPAA, and even the more niche FINRA requirements.
Performance Meets Compliance: The Unexpected Bonus
Many think dedicated servers are a performance trade‑off for security, but the reality is the opposite. Without noisy neighbors, you get predictable I/O latency and consistent CPU cycles—crucial for workloads like real‑time fraud detection or medical imaging analysis.
If you need a deeper dive into why dedicated servers excel at low‑latency workloads, check out Dedicated Servers: The Unseen Engine Driving Real‑Time Data Success. The principles that make them perfect for high‑speed data pipelines also make them ideal for compliance‑heavy environments where performance bottlenecks can become regulatory breaches.
Hybrid Cloud Strategies: Bridging the Gap Without Compromise
Most enterprises aren’t going “all‑in” on dedicated servers. Instead, they’re building a hybrid model: sensitive workloads stay on dedicated hardware, while less‑critical services run in the public cloud. This approach gives you the best of both worlds—scalability where you need it, and control where you don’t.
Key considerations for a compliant hybrid architecture:
- Secure Connectivity: Deploy dedicated VPNs or Direct Connect equivalents to ensure encrypted, low‑latency links between your dedicated rack and the cloud provider.
- Consistent Identity Management: Use a single identity provider (IdP) that spans both environments, enforcing MFA and role‑based access controls everywhere.
- Data Classification: Tag data at rest with sensitivity labels that dictate whether it can be migrated to the cloud or must remain on‑prem.
When you orchestrate these elements correctly, you get a compliance‑first architecture that still benefits from cloud innovation. For a perspective on handling latency in distributed setups, see Turning Global Latency Challenges into Opportunities with Geo‑Distributed Cloud Hosting.
Cost Predictability: Turning CapEx Into Opex Without the Surprise
One of the biggest myths about dedicated servers is that they’re prohibitively expensive. In reality, the cost model is highly predictable. You pay a fixed monthly fee for rack space, power, and network, plus a transparent hardware refresh schedule. There’s no surprise bill for “bursting” traffic or “data egress” fees that can cripple a compliance budget.
For regulated businesses, that predictability translates to smoother budgeting for audit cycles, security tooling, and incident response plans. Moreover, many providers now offer managed dedicated services that bundle patch management, backup, and 24/7 SOC monitoring—turning a pure CapEx expense into a manageable Opex line item.
Choosing the Right Provider: What to Look For
Not all dedicated hosting is created equal. Here’s a quick checklist to ensure the provider you pick can truly support a compliance‑first strategy:
- Certification Portfolio: Look for ISO 27001, SOC 2 Type II, PCI‑DSS Level 1, and any regional certifications (e.g., FedRAMP for US government work).
- Physical Security Controls: Biometric access, CCTV, guard patrols, and man‑traps should be standard.
- Network Isolation Options: Ability to provision dedicated firewalls, VLANs, and private interconnects.
- Hardware Lifecycle Transparency: Clear policies for end‑of‑life, firmware updates, and secure de‑provisioning.
- Compliance Support: Dedicated compliance engineers or partners who can help you map controls to frameworks.
Choosing wisely not only keeps you compliant but also future‑proofs your infrastructure as regulations evolve.
Real‑World Case Study: A Healthcare Provider’s Journey
Consider HealthFirst, a regional healthcare network handling over 5 million patient records. Their legacy on‑prem data center was aging, and the cost of maintaining compliance was spiraling. They migrated their EMR (Electronic Medical Records) platform to a dedicated server farm located in a HIPAA‑compliant data center.
Key outcomes:
- Audit Pass Rate: 100% pass on the next HIPAA audit, thanks to immutable logs and hardware encryption.
- Performance Boost: 30% reduction in query latency for imaging archives, directly improving physician workflow.
- Cost Savings: 22% reduction in total cost of ownership over three years, due to predictable pricing and reduced need for third‑party security consultants.
HealthFirst’s story illustrates how dedicated servers can be a catalyst for both compliance and operational excellence.
Getting Started: A Pragmatic Roadmap
If you’re ready to explore dedicated server hosting for compliance, follow this three‑step roadmap:
- Assess Your Compliance Landscape: Catalog all regulations affecting your data, map each to technical controls, and identify which workloads require isolation.
- Pilot a Critical Workload: Choose a high‑risk application (e.g., payment processing) and migrate it to a dedicated server in a certified data center. Measure security metrics, performance, and cost.
- Scale with Governance: Build a governance model that includes regular audits, patch cycles, and a clear hardware refresh schedule. Leverage managed services if your team lacks deep sysadmin expertise.
By taking a measured, compliance‑centric approach, you can unlock the security benefits of dedicated servers without disrupting your broader IT strategy.
Conclusion: The Strategic Imperative of Dedicated Servers
Regulated industries can no longer afford to treat hosting as a commodity. The stakes—financial penalties, reputational damage, and patient or customer harm—are simply too high. Dedicated server hosting offers a tangible, auditable, and performance‑rich foundation that aligns perfectly with the rigorous demands of compliance frameworks.
Whether you’re a CIO wrestling with data‑sovereignty, a security officer needing immutable logs, or a finance leader tasked with predictable budgeting, dedicated servers give you the control you need—and the peace of mind you deserve. The future isn’t about abandoning the cloud; it’s about building a hybrid ecosystem where dedicated hardware anchors the most sensitive parts of your business.
Shawn DesRochers is a certified Microsoft technician and Programmer with 30+ year's experience. He has written many reviews on computer related products, software, and SEO related topics. When he's not writing reviews he can be found at one of the Oldest Directories Online Invision Graphics Directory which he is the CEO of. Shawn is a FULL Stack Web Developer. So if you have a project and need assistance dont hesitate to reach out.
Related Posts
Dedicated Servers: The Strategic Backbone for High‑Performance Enterprise Workloads
Dedicated servers provide isolation, predictable billing, and granular hardware control, making them... Read More
Dedicated Servers: The Unsung Hero of Real‑Time Data Pipelines
Real‑time analytics demand sub‑millisecond latency, predictable resources, and tight security. T... Read More
Zero‑Trust Starts with the Server You Own
Dedicated servers provide the physical isolation, micro‑segmentation, and continuous telemetry ess... Read More
Top Posts
Feature Flagging as a Growth Engine: Experiment Safely at SaaS Scale
Feature flags transform every deployment into a low‑risk experiment, enabling rapid iteration, data‑driven decision‑making, and seamless revenue loops for...Read More
The Hidden Power of Shared Web Hosting for Growing SaaS Startups
Shared web hosting often gets dismissed by SaaS founders, but it offers a low‑cost, secure, and surprisingly performant foundation. This post reveals why itâ€...Read More
Full‑Stack Observability: Turning Data Into Real‑Time Development Feedback
Full‑stack observability stitches together frontend performance, backend latency, and infrastructure metrics into a single, actionable narrative, enabling fas...Read More
Composable Commerce: Crafting a Modular Marketplace That Scales
Composable commerce lets businesses assemble a marketplace from best‑in‑class services, delivering flexibility, faster experiments, and seamless scaling whi...Read More
0 Comments
Post Comment
You will need to Login or Register to comment on this post!